+/ STATUS: OPERATIONAL · EBPF_TRACING · LINUX_5.8+ · HARTWELL_LABS
TALUS_PROCESS
_MONITOR
// SYS: RUST · eBPF · GO · KERNEL_TRACING · AUTO_RESPONSE
// WHY: FILE_ENCRYPTION_EVENTS // CAUGHT_IN_KERNEL
A sliding-window heuristic over the syscalls ransomware cannot hide — execve, openat, unlink — traced live in-kernel. Detection and response in one binary, before the encryption finishes.
/ What it is
Talus is a Rust eBPF monitor that watches filesystem-destroying syscall patterns in real time and acts on them — no signatures, no daemon sprawl, one GHCR image. The detection core scores a sliding window over traced syscalls; when the pattern of a ransomware run shows up, response fires automatically.
- Built
- Rust core, Go collector, eBPF probes
- Target
- Linux 5.8+, CI-built GHCR image
- Detection
- Sliding-window heuristics, no signatures
- Status
- Open source, MIT, CI green
[01] // FEATURES
WATCH_THE_KERNEL,
KILL_FAST.
eBPF probes
execve/openat/unlink traced live in-kernel — zero-copy ringbuffers.
Sliding-window core
Heuristic scoring over syscall streams — no signatures to update.
Automated response
When the ransomware pattern fires, response actions run without a human in the loop.
Live TUI
Terminal dashboard with the alert stream as it happens.
GHCR deploy
CI-built container image — pull and run on any 5.8+ host.
Open source
MIT, four green workflows: Rust CI, CI, GHCR, Scorecard.
[02] // DEPTH
HOW_IT
WATCHES.
« Encryption leaves a fingerprint in the syscall stream. Talus reads it before the last file dies. »
Probe layer
eBPF programs attach to the syscall surface and stream events into ringbuffers — no LD_PRELOAD, no patching.
Detection core
Rust scores a sliding window over the stream; bulk-rename/encrypt/delete patterns rise above the noise floor.
Response engine
On detection: automated response actions plus the live TUI alert stream for the operator.
[03] // HUB
FIND_IT_
AROUND_THE_WEB.
[04] // SUBPAGES
DEPLOYED_ON_
GH_PAGES.
[05] // PROOF // SHIPPED_AND_RUNNING
PROOF_OF_WORK.
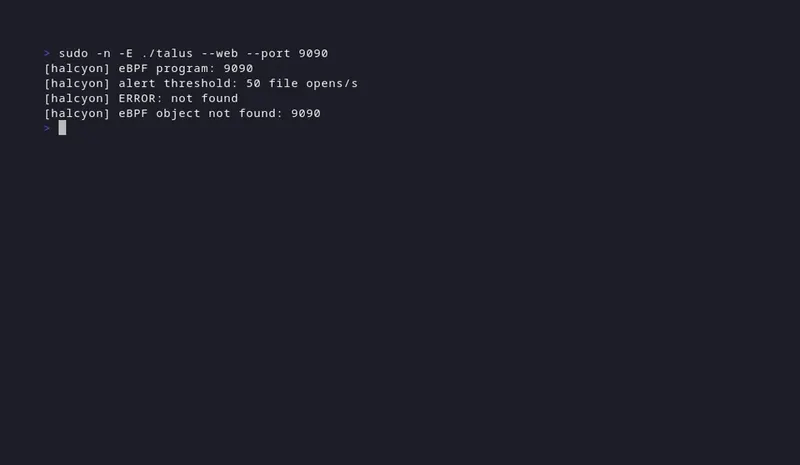
Real captures from running the tool on this machine. No mockups.
[06] // BLOG // WRITEUPS
Write-ups live in /blog/ — full archive with reddit-grade voting, accounts and discussions under every post.